← All tools

pCapitan Admiral

Everything in pCapitan, plus the full forensic investigation arsenal, for DFIR, identity security, audits and court-ready casework.

pCapitan Admiral is the full forensic investigation platform. It carries the whole of pCapitan, reading any capture in plain language with the evidence behind every answer, and adds the bench a serious inquiry needs.

It assesses your Active Directory, certificate services and Group Policy offline, against every compromise technique in the Five Eyes joint advisory, and maps each finding to the NIST, ISO 27001 and PCI-DSS controls your auditors check. It triages malware without running it, hunts an indicator across every capture in a case, learns what is normal so the unusual stands out, and keeps an evidence trail with trusted timestamps that stands up in court.

It is made for DFIR examiners, Active Directory and identity-security specialists, security auditors, malware and threat analysts, threat hunters, and compliance and expert-witness work.

Admiral is a separate app with its own licence. It installs beside pCapitan or on its own, and an Admiral key does not unlock pCapitan, nor a pCapitan key Admiral. Try every feature free for 14 days; the overview walks through what it adds.

Requirements: Windows 10 or 11 (64-bit), or Linux (any distribution with glibc 2.31 or later for the AppImage). Live capture and the full protocol dissection use free, open-source capture components; the user guide inside the app shows how to add them in a minute.

pCapitan Admiral in pictures

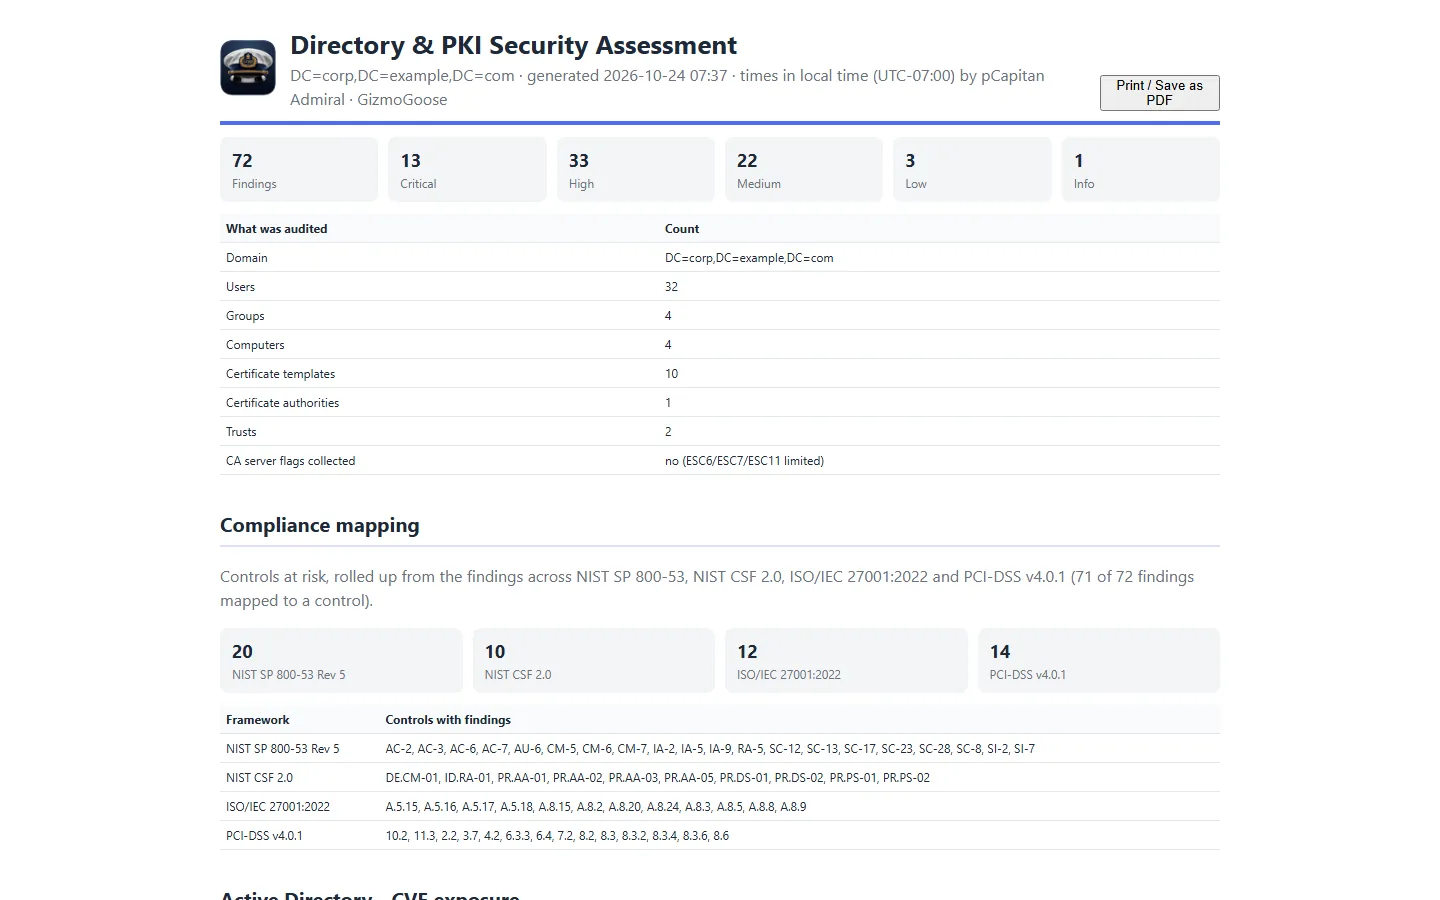
Directory & PKI assessment, mapped to NIST, ISO 27001 and PCI-DSS controls
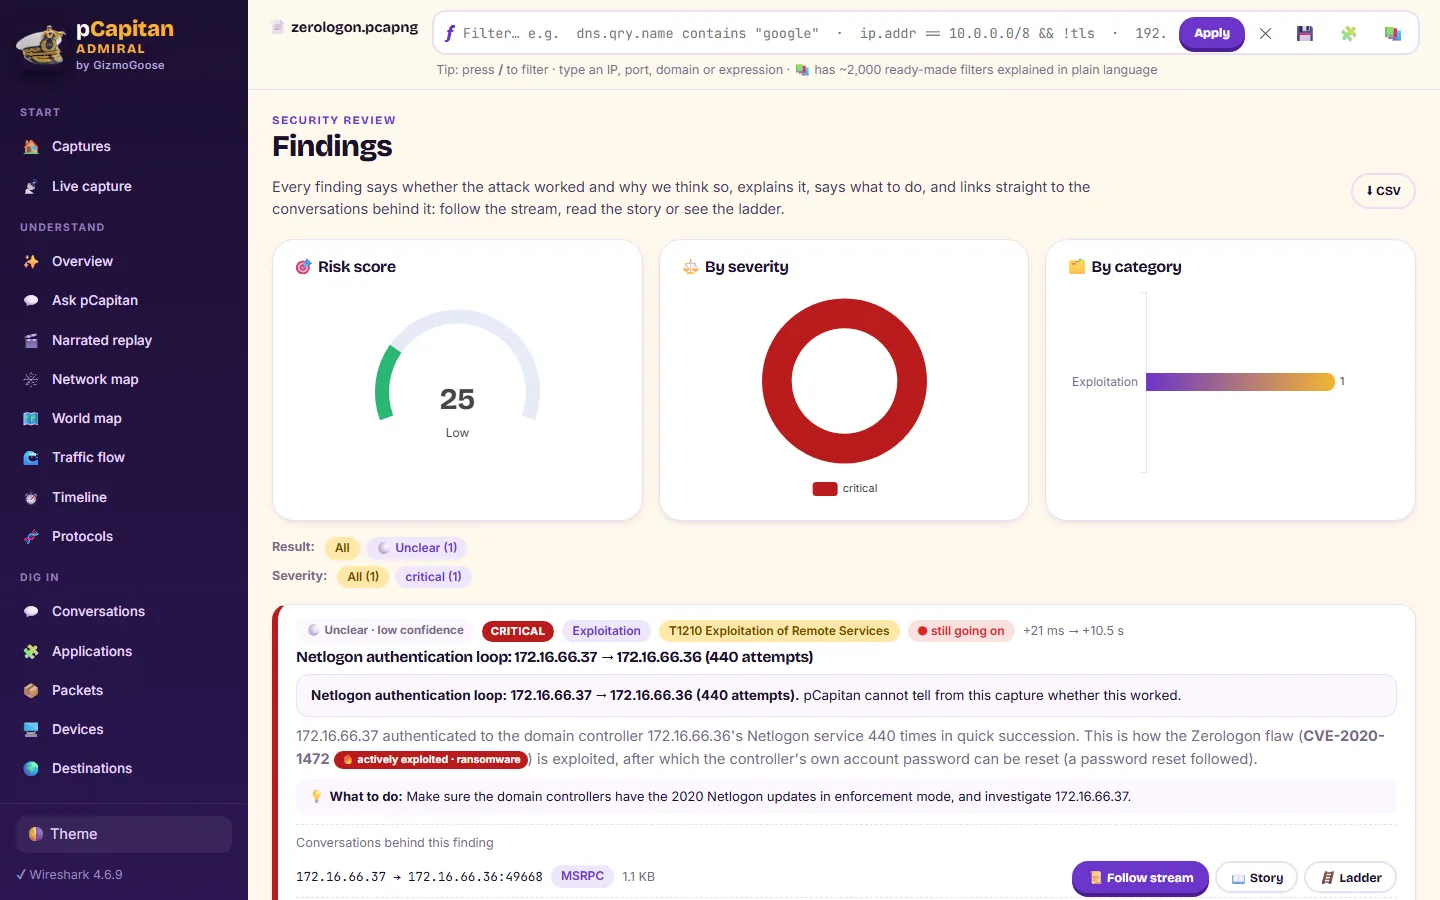
Active Directory attacks seen in the traffic, explained with what to do
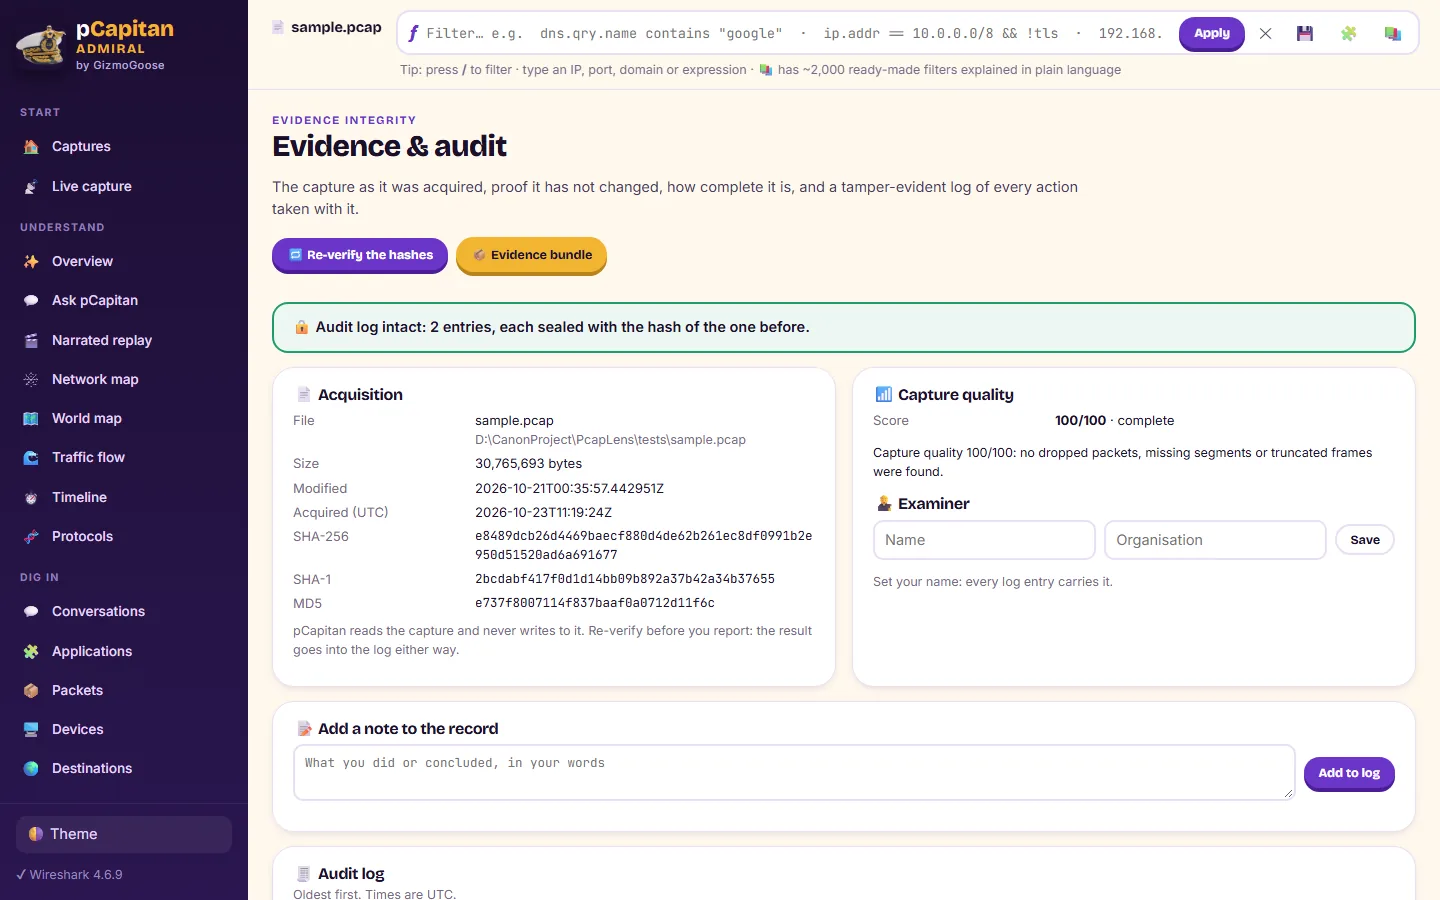
Court-ready evidence: hash-chained audit log and chain of custody
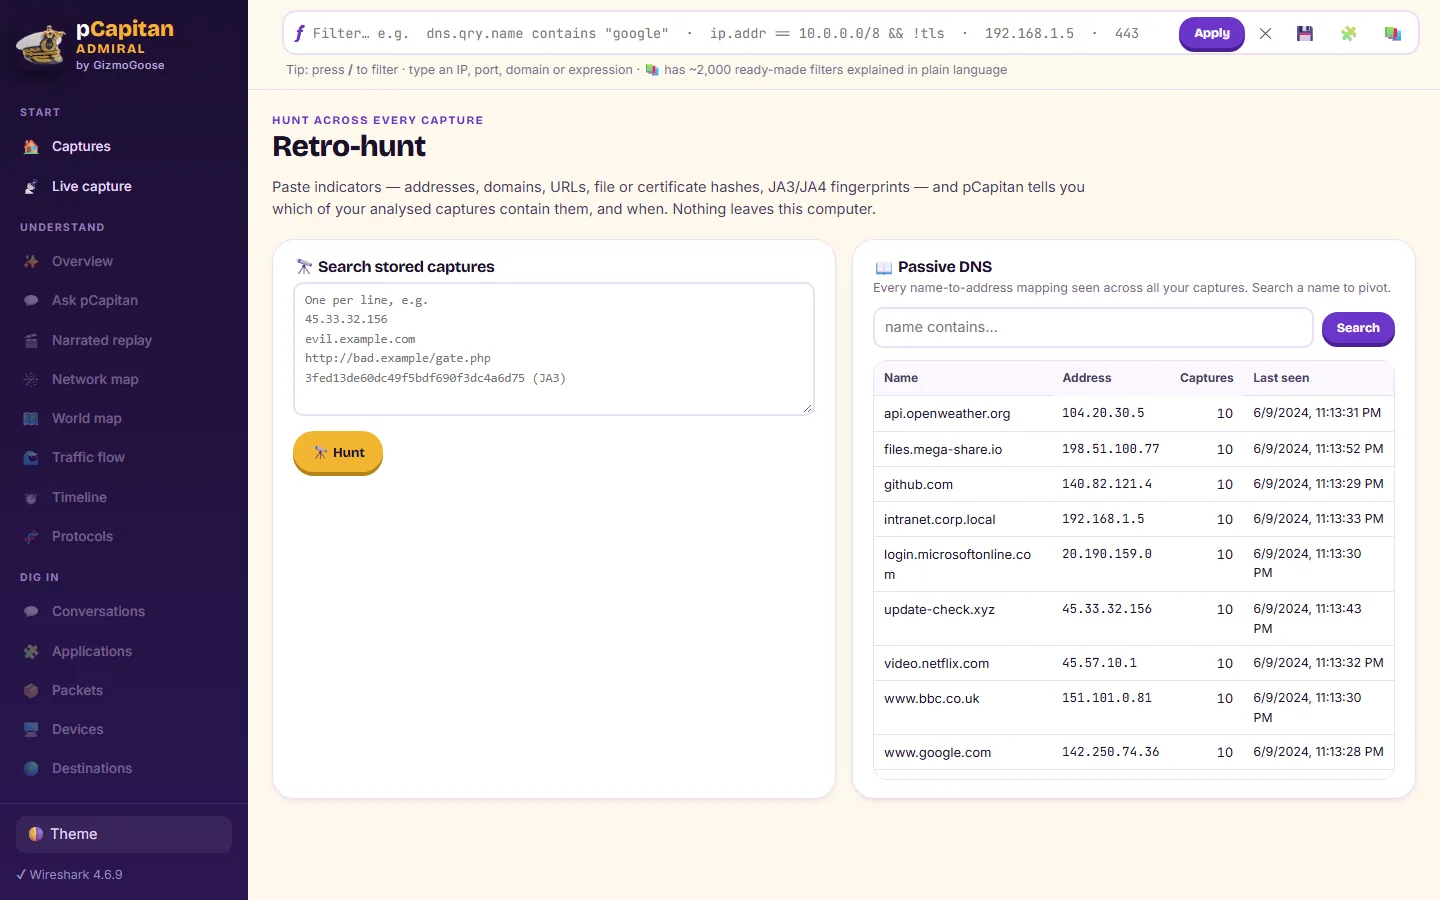
Retro-hunt an indicator across every capture in the case at once
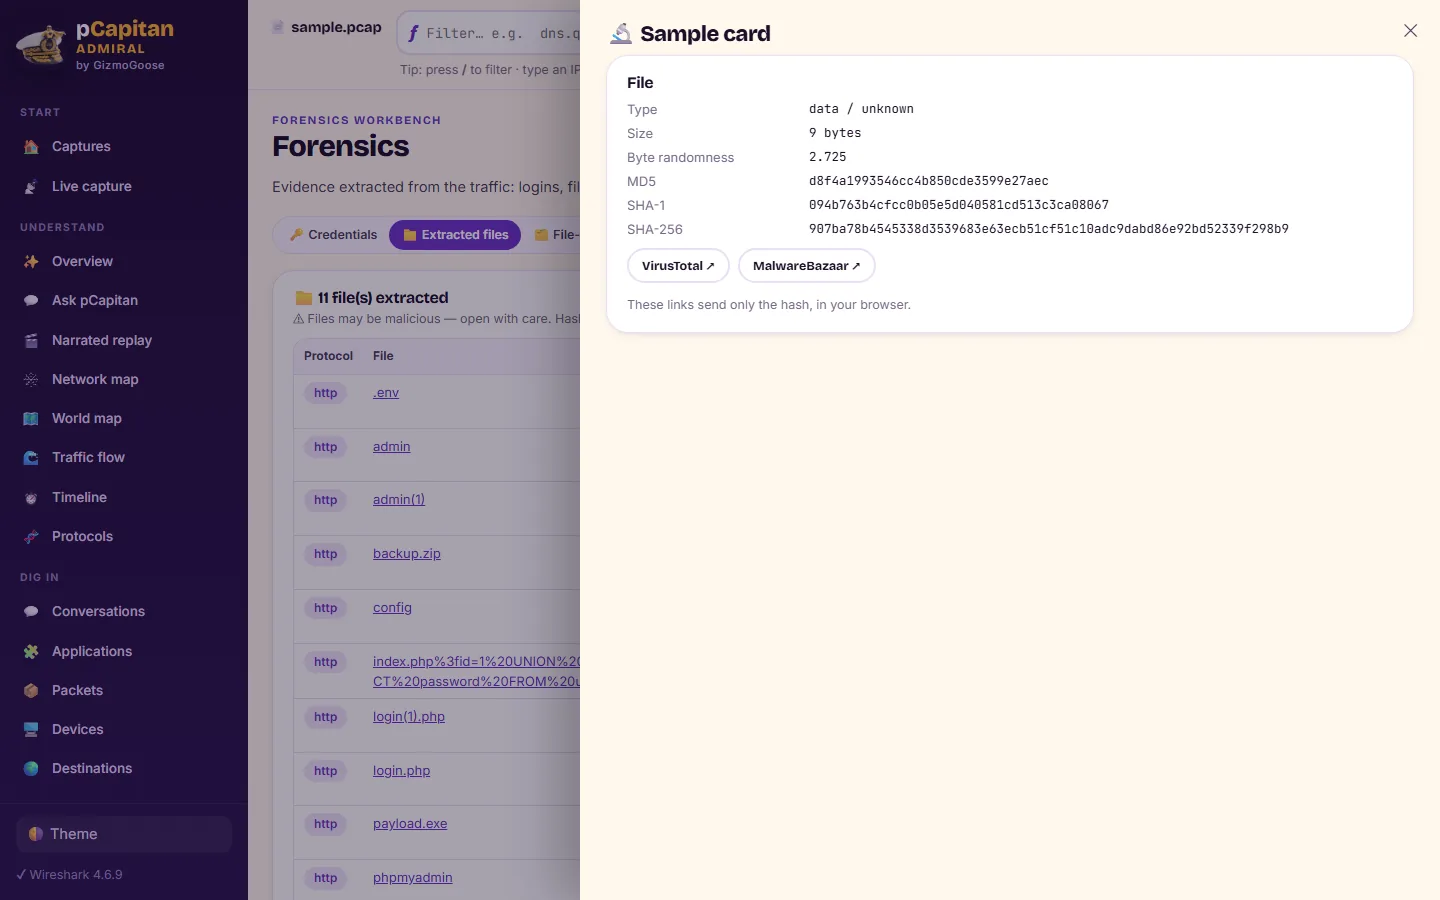
Malware static-triage sample card, without ever running the file
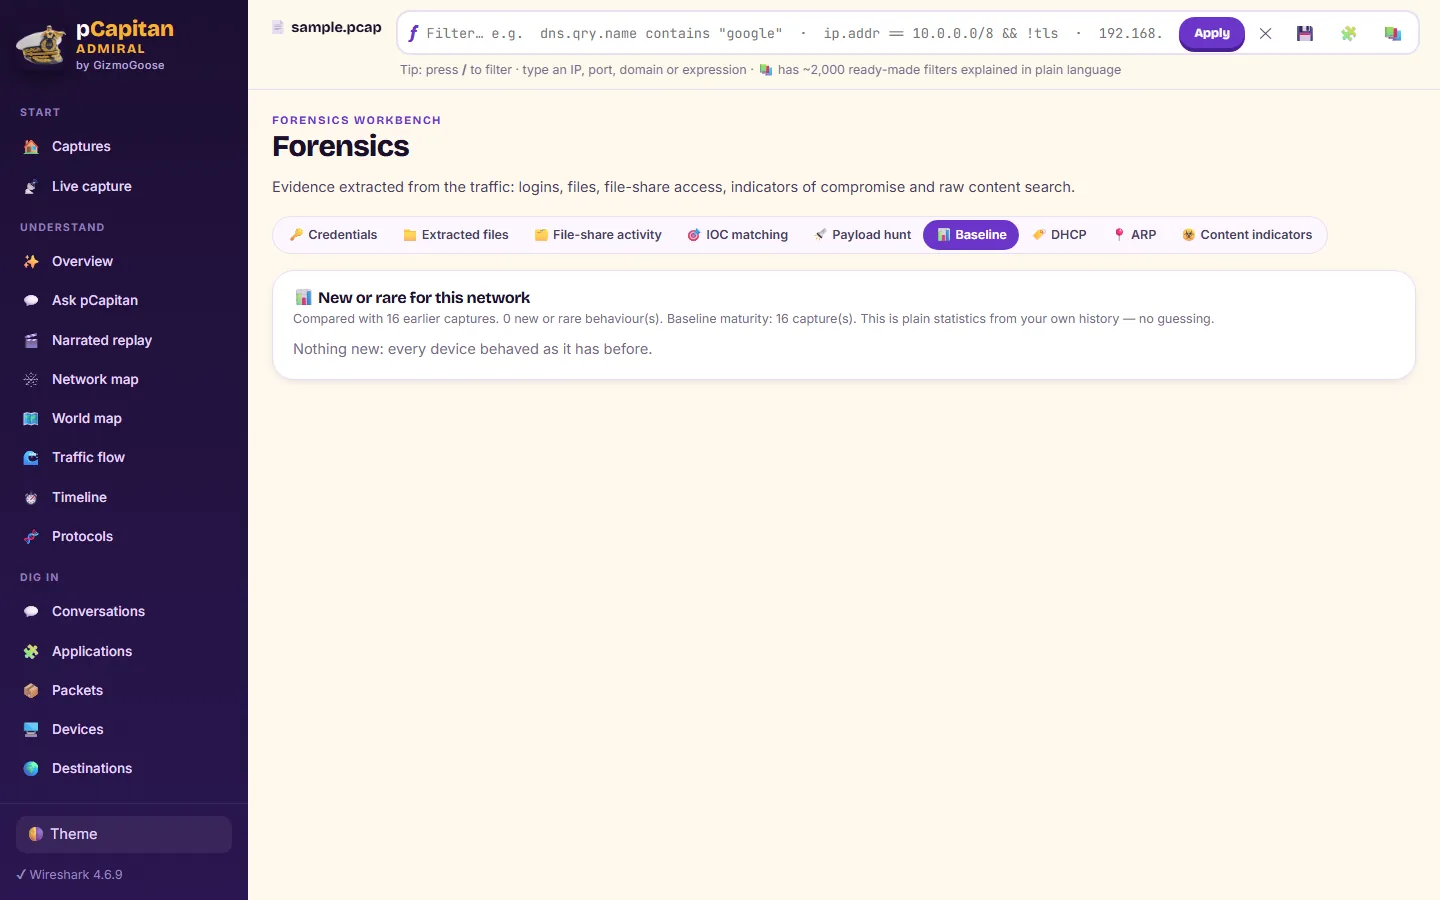
Baselines across captures: what is new or rare stands out
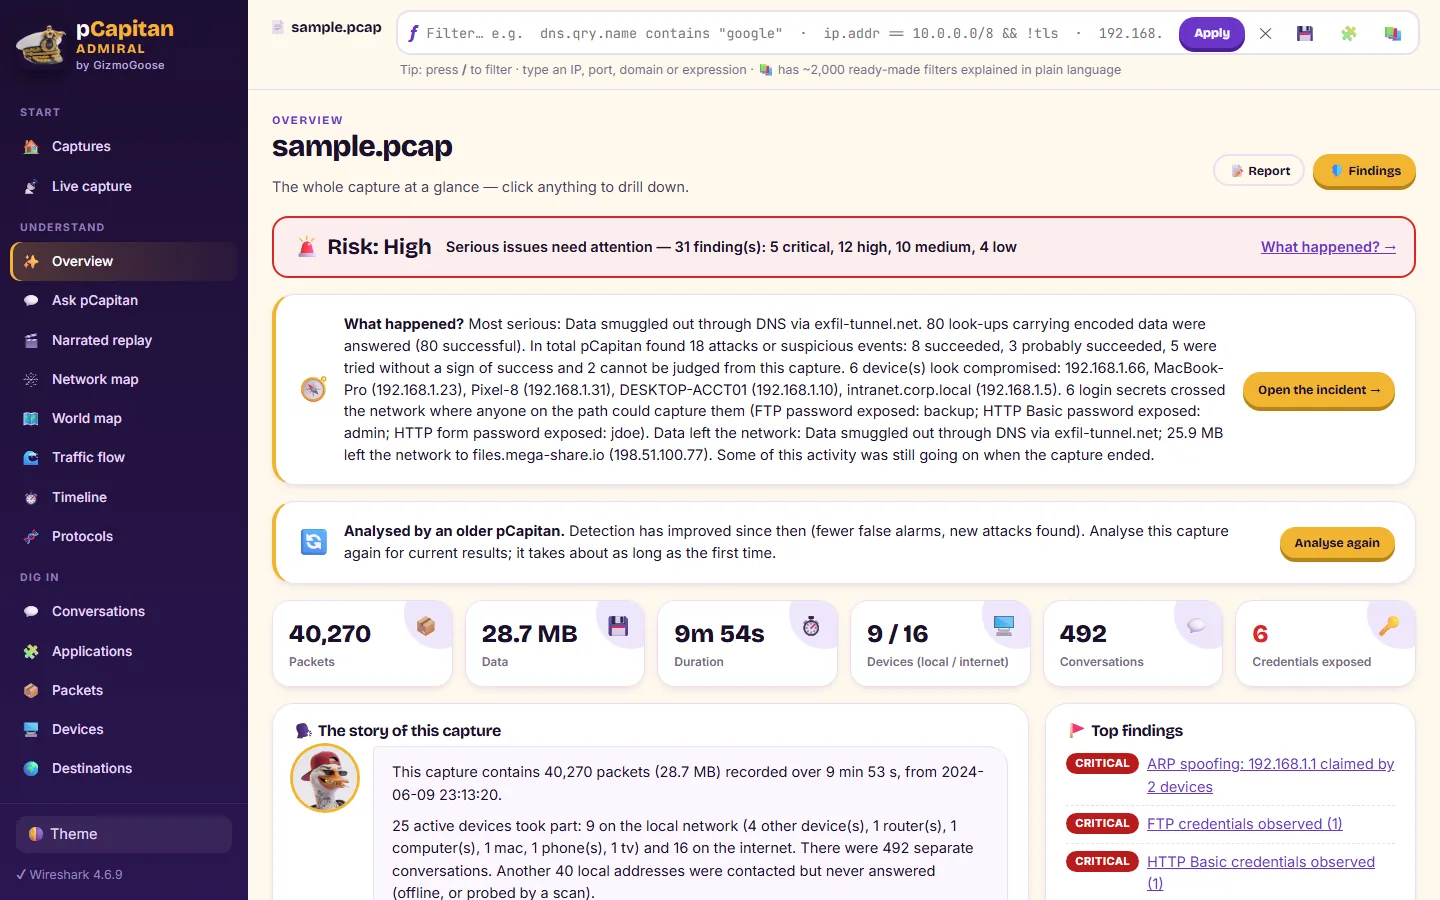
The overview: risk level, the story of the capture and the top findings
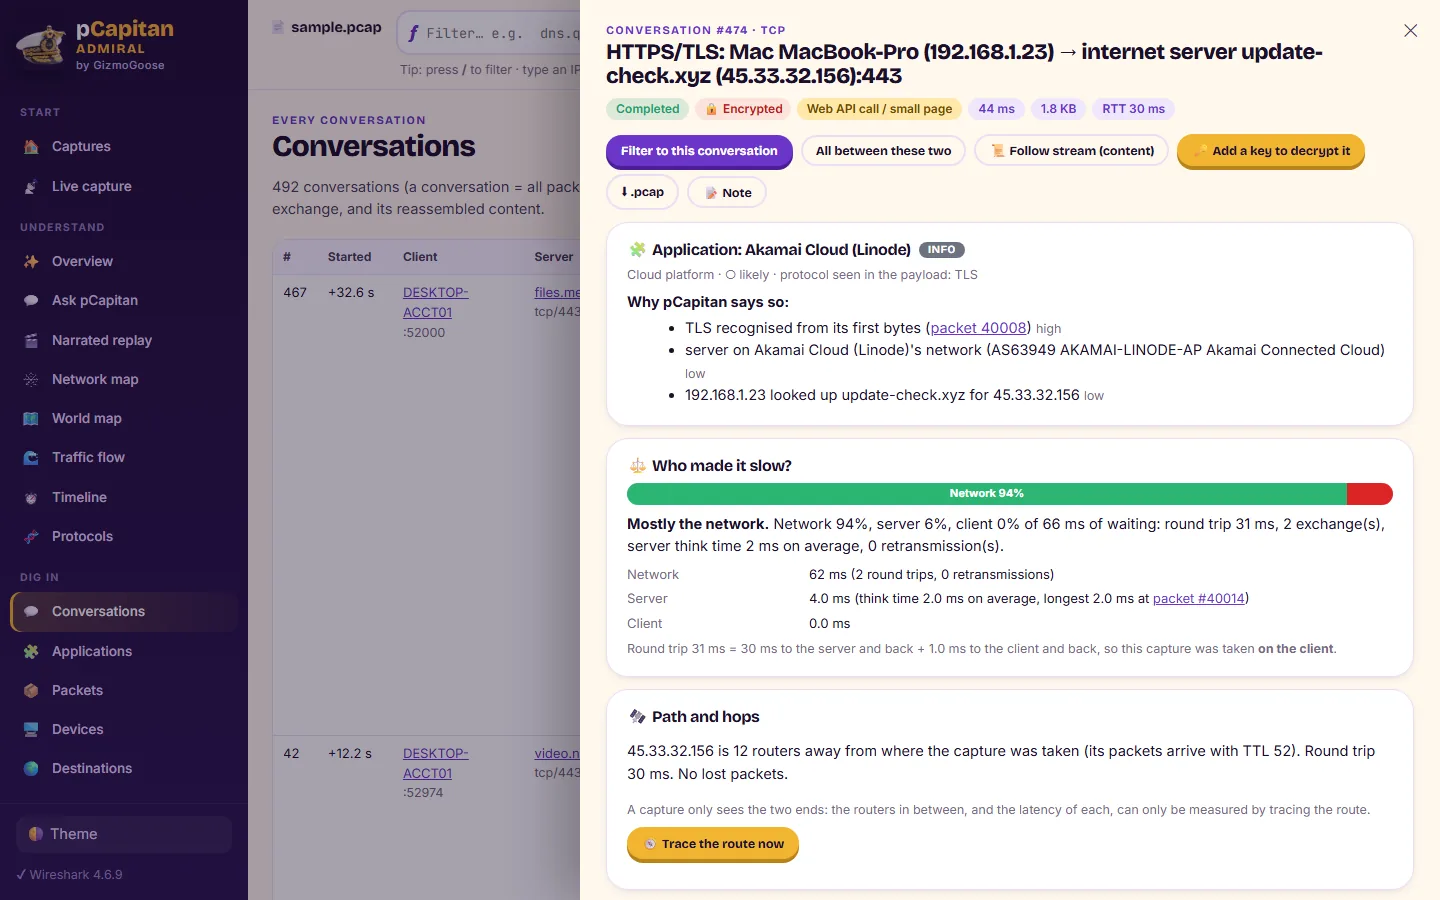
The story of one conversation, step by step

Directory & PKI assessment, mapped to NIST, ISO 27001 and PCI-DSS controls

What it does

  • Everything in pCapitan, from the deep packet inspection engine and the incident story to reports and live capture
  • Offline Active Directory, certificate-services (AD CS) and Group Policy assessment, checked against all 17 compromise techniques in the Five Eyes joint advisory
  • Every finding mapped to NIST SP 800-53, NIST CSF 2.0, ISO/IEC 27001 and PCI-DSS controls, with a per-control summary
  • Group Policy security benchmarks (CIS and DISA STIG), and recovery of passwords left in Group Policy Preferences
  • Court-ready evidence and chain of custody: a hash-chained audit log with trusted timestamps (RFC 3161)
  • Malware static-triage sample cards that summarise a suspicious file at a glance, without running it
  • Case-level retro-hunt across every capture and passive DNS, with cross-capture baselines

Every feature

Active Directory and certificate services

  • An offline security assessment of your Active Directory and its certificate services (AD CS): misconfigurations, known weaknesses and signs of compromise, in plain words with what to fix first. A normal domain account is enough; nothing is ever changed
  • Checked against the Five Eyes advisory: every one of the 17 Active Directory compromise techniques, from Kerberoasting to Golden SAML, reported directly where the directory or the traffic shows it, and as the weakness that makes it possible where it does not
  • Passwords left in Group Policy Preferences, found and decrypted so you can remove them and change those passwords
  • The whole certificate ladder: every known template and CA weakness (ESC1 to ESC16), the inventory of every certificate your CA has issued or revoked, and a live check of your revocation lists and OCSP responders
  • Attacks seen in the traffic: forged Kerberos tickets, a rogue domain controller (DCShadow), directory replication from a non-domain-controller (DCSync), certificate logons and copies of the Active Directory database
  • A native Active Directory MS-RPC engine, and FreeIPA identity-management servers assessed the same way

Audits and compliance

  • Every finding mapped to the controls auditors check: NIST SP 800-53 Rev 5, NIST CSF 2.0, ISO/IEC 27001:2022 and PCI-DSS v4.0.1, with the controls at risk and the findings behind each
  • Group Policy benchmarks: password and lockout policy, dangerous user rights, anonymous access, LAN Manager hashes, User Account Control and auditing, checked against CIS and DISA STIG
  • The printable report includes the compliance summary, ready to hand to an auditor

Malware and threat analysis

  • Malware static-triage sample cards: what a suspicious file is, what it touches and why it matters, without ever running it
  • Command-and-control framework fingerprinting in the traffic
  • Sigma detection-as-code: your own rules in the open Sigma format, run across the evidence

Hunting across a whole case

  • Case-level retro-hunt of every loaded capture, together with passive DNS, for an indicator or a pattern in a single pass
  • Cross-capture baselines, so what is new or rare for a device or a network stands out
  • A case made of many captures analysed together and read as a single story

Court-ready evidence

  • A hash-chained audit log of every step of the investigation, tamper-evident from start to finish
  • Trusted timestamps (RFC 3161) that prove when each piece of evidence was handled
  • A chain of custody and an evidence bundle built to stand up in court

Everything in pCapitan

  • Plain-language analysis of any capture: devices, applications, conversations and risks, with the evidence behind every answer
  • A deep packet inspection engine for about 1,400 applications, more than 100 detectors and IDS rules
  • Every attack judged (succeeded, attempted or failed), patient zero and blast radius
  • The Decryption Vault, VoIP, maps, compare, batch audit, reports and live capture

Private and yours

  • Runs on your own computer; captures and directory data never leave it
  • A 14-day free trial with every Admiral feature
  • Pay once, no subscription; one computer at a time, and you move it yourself

pCapitan or pCapitan Admiral?

Everything in pCapitan, plus the full forensic investigation arsenal, for DFIR, identity security, audits and court-ready casework.

Network forensics · sold separately from Admiral

pCapitan

A forensic analyst in a box. pCapitan reads a capture file or live traffic and tells the whole story in plain language, from devices and applications to attacks and their outcome, with the proof one click away. It runs entirely on your computer.

What you get

  • A built-in deep packet inspection engine identifies about 1,400 applications, even inside encrypted traffic, and shows the evidence behind every name
  • Every attack judged: succeeded, attempted or failed, with the proof packets, patient zero and how far it spread
  • More than 100 detectors, from hidden payloads and jitter-masked command channels to industrial control commands
  • Type a question in plain words and get the answer worked out from the capture by fixed rules, with the evidence

Who it's forSecurity and network engineers, SOC analysts, incident responders, managed service providers and IT teams, and anyone handed a capture who needs clear answers fast.

  • Windows · Linux
  • v1.7.2
  • 14-day free trial

$39.99 once

Buy pCapitan

New · sold separately from pCapitan

pCapitan Admiral

The complete forensic platform. Admiral adds an offline assessment of your Active Directory, certificate services and Group Policy, checked against every compromise technique in the Five Eyes advisory and mapped to NIST, ISO 27001 and PCI-DSS, plus malware triage, case-wide hunting and court-ready evidence.

Everything in pCapitan, plus

  • Offline Active Directory, certificate-services (AD CS) and Group Policy assessment, checked against all 17 compromise techniques in the Five Eyes joint advisory
  • Every finding mapped to NIST SP 800-53, NIST CSF 2.0, ISO/IEC 27001 and PCI-DSS controls, with a per-control summary
  • Group Policy security benchmarks (CIS and DISA STIG), and recovery of passwords left in Group Policy Preferences
  • Court-ready evidence and chain of custody: a hash-chained audit log with trusted timestamps (RFC 3161)

Who it's forDFIR examiners, Active Directory and identity-security specialists, security auditors, malware and threat analysts, threat hunters, and compliance and expert-witness work.

  • Windows · Linux
  • v1.7.2
  • 14-day free trial

$84.99 once

Buy Admiral

pCapitan

For the engineer who needs the truth of a capture in minutes, not hours. pCapitan reads any capture in plain English — every device, every conversation, every threat — and writes the report for you. It is the fast, defensible answer for IT and security teams, SOC analysts and incident responders who work one capture at a time, entirely on their own computer, for a single one-time price.

pCapitan Admiral

For the investigator who commands a case, not merely a file. Admiral carries the whole of pCapitan and adds the forensic bench a serious inquiry demands: an offline assessment of your Active Directory, PKI and Group Policy, mapped to the controls your auditors check, a malware-triage lab, hunting and baselining across every capture you hold, and an evidence trail that stands up in court. It is built for DFIR examiners, Active Directory and identity-security specialists, malware and threat analysts, threat hunters, and compliance and expert-witness work — the same plain-language clarity, raised to the scale of an investigation.

Volume licenses. For SOCs, DFIR teams and agencies. One key for many computers, installed silently and managed centrally, with or without Admiral. Ask for a quote

Compare the editions

CapabilitypCapitanAdmiral
In both pCapitan and Admiral
Plain-language analysis of any capture ✓✓
100+ threat, anomaly & hygiene detectors ✓✓
Deep packet inspection (~1,400 applications) ✓✓
Decryption Vault (TLS, Wi-Fi, IPsec) ✓✓
Encryption & certificate insight (JA3/JA4, TLS/QUIC) ✓✓
Incident story & "did the attack work?" ✓✓
Known-vulnerability (CVE) exposure per device ✓✓
Reports, exports, your branding & vendor-safe copy ✓✓
Live & remote capture ✓✓
Filters, maps, VoIP, logins & routing, compare, batch ✓✓
Only in pCapitan Admiral
Offline Active Directory, Microsoft PKI (AD CS) & Group Policy security assessment –✓
Checked against all 17 AD compromise techniques in the Five Eyes joint advisory –✓
Compliance mapping: NIST SP 800-53, NIST CSF 2.0, ISO/IEC 27001:2022, PCI-DSS v4.0.1 –✓
Group Policy benchmarks (CIS, DISA STIG) & Group Policy Preferences password recovery –✓
Forged Kerberos tickets, DCShadow & AD database theft detection –✓
Live CRL & OCSP health of your certificate authorities –✓
FreeIPA identity-management assessment –✓
Native Active Directory MS-RPC attack engine –✓
Malware static-triage sample cards –✓
Case-level retro-hunt across every capture + passive DNS –✓
Cross-capture baselines (what's new or rare for a device) –✓
Court-ready evidence & chain of custody (hash-chained audit log + RFC 3161 timestamps) –✓
Command-and-control framework fingerprinting –✓
Sigma detection-as-code –✓
One analysis runs every loaded source together –✓
Price$39.99 once$84.99 once

Two separate purchases. pCapitan and pCapitan Admiral each come with their own purchase key ($39.99 and $84.99). pCapitan Admiral already includes everything in pCapitan, so there is no upgrade: if you want pCapitan Admiral, buy it on its own.

Goose-approved. Pay $84.99 once and pCapitan Admiral is yours. No subscription, no honking around.